Control After Email Delivery
ORQET investigates reported emails, delivers human-derived verdicts, automates remediation, and produces threat intelligence.
Every organization invests in technology to stop threats before delivery, yet email threats still bypass those preventive controls and are delivered to users. What happens next defines the outcome.
ORQET confirms whether the email is malicious, removes it from every mailbox it reached, and turns the indicators it extracts into threat intelligence your team can use. ORQET makes that process repeatable, measurable, and scalable.
Human Judgment, Applied at Scale
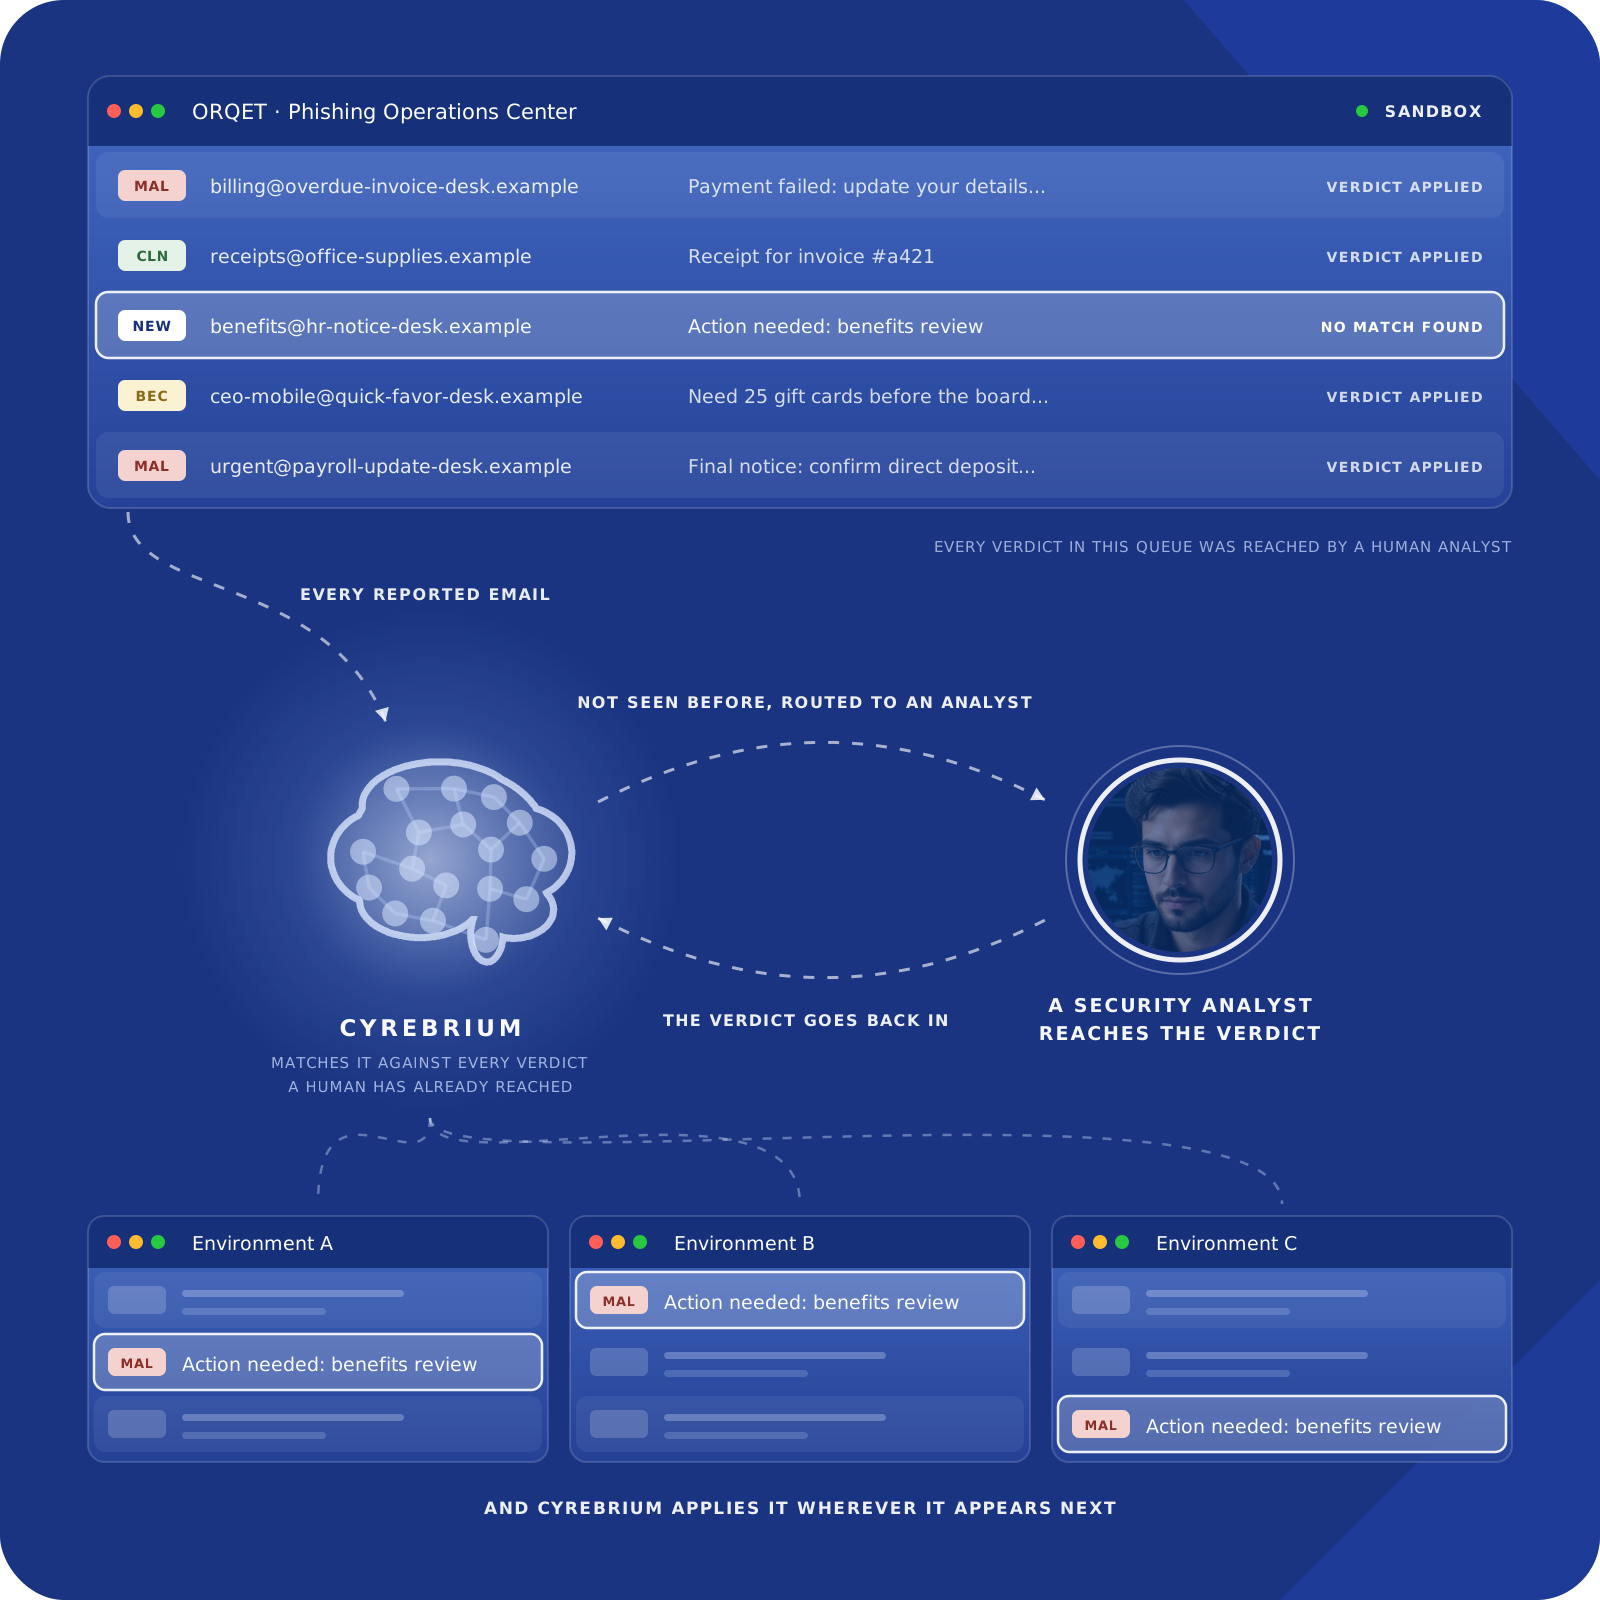
Cyrebrium is ORQET’s AI-assisted matching and automation engine, combining technology with human expertise to apply human-derived verdicts faster and more consistently while keeping human judgment at the center of the process.
When a reported email matches one that has already been reviewed, Cyrebrium learns and applies the verdict previously reached by a human analyst. When an email has not been seen before, it is routed directly to a security analyst for review. Every verdict traces back to human judgment, allowing Cyrebrium to accelerate the process without replacing the human expertise behind it.
As more emails are reviewed, the library of human-derived verdicts grows. Intelligence gained from a threat in one customer environment can be applied when the same threat appears in another, allowing Cyrebrium to recognize previously analyzed emails and apply established human-derived verdicts across ORQET customer environments.
Powered By Cyrebrium
Human Judgment, Applied at Scale
Cyrebrium is ORQET’s AI-assisted matching and automation engine, combining technology with human expertise to apply human-derived verdicts faster and more consistently while keeping human judgment at the center of the process.
When a reported email matches one that has already been reviewed, Cyrebrium learns and applies the verdict previously reached by a human analyst. When an email has not been seen before, it is routed directly to a security analyst for review. Every verdict traces back to human judgment, allowing Cyrebrium to accelerate the process without replacing the human expertise behind it.
As more emails are reviewed, the library of human-derived verdicts grows. Intelligence gained from a threat in one customer environment can be applied when the same threat appears in another, allowing Cyrebrium to recognize previously analyzed emails and apply established human-derived verdicts across ORQET customer environments.
Detection
Reported emails arrive fully indexed, searchable by sender, subject, or attachment.

Validation
A security analyst renders the verdict, with the supporting evidence recorded so the decision can be explained later.
Response
Confirmed threats are located across every affected mailbox and removed in one action, with each remediation tracked.
Intelligence
Indicators and investigative context from analyzed attacks are captured, enriched, and distributed so each verdict informs the next.
The Missing Layer in Email Security
A reported email has to be investigated. A real threat must be distinguished from a false alarm.
Most security programs are built to keep threats out. Fewer are built for what happens when one gets in. That moment is where confidence is won or lost.
A decision has to be made, acted on, and remembered so that the next incident is handled faster than the last. Skip any of that, or rely on disconnected tools to do it, and the organization loses something it cannot get back: the knowledge each incident should have produced.
Like every automated detection engine, even the most advanced systems will let something through. That is not a flaw worth hiding. It is the reason Post-Delivery Email Threat Response exists, and it is the gap ORQET was built to close.
Prevent
Reduce the number of threats reaching the inbox.
DETECT
Identify reported and detected threats that require investigation.
VALIDATE
Determine what is safe, what is malicious, and what requires action.
RESPOND
Deliver coordinated response to reduce risk and organizational exposure.
IMPROVE
Transform every trusted decision into threat intelligence.
ORQET’s intelligence is not built on automation alone. It is built on years of trusted investigations, human analyst expertise, structured investigative workflows, verified indicators of compromise, and signal correlation across every threat ORQET has helped investigate or resolve. Every confirmed decision sharpens the model behind it, drawn from human investigations rather than theoretical data. The result is that intelligence organizations can trust it, not because it claims to be intelligent, but because every decision it informs can be explained and traced back to a verified outcome.
Post-Delivery Email Threat Response closes the gap automated detection leaves behind. As a Post-Delivery Email Threat Response platform, ORQET turns every reported and detected threat into a trusted coordinated response, and intelligence the organization keeps. The result compounds: the maturity improves, resilience strengthens, and confidence increases over time.
The real question is how to make that happen consistently, regardless of environment. That is where ORQET’s approach comes into focus.
Where ORQET Fits in Your Security Ecosystem
One Platform, Connected to Your
Security Operation
ORQET enhances and works alongside the security technologies organizations already rely on. Your existing security stack remains the first line of defense against threats before they reach the inbox; ORQET handles what happens after an email is reported.
Every reported email enters the same workflow: ORQET delivers a human-derived verdict, automatically purges confirmed malicious emails from affected mailboxes, and captures tactical and technical threat intelligence to strengthen future response.
This is where ORQET fits: after delivery, working alongside the security stack you already manage to extend protection beyond the inbox.
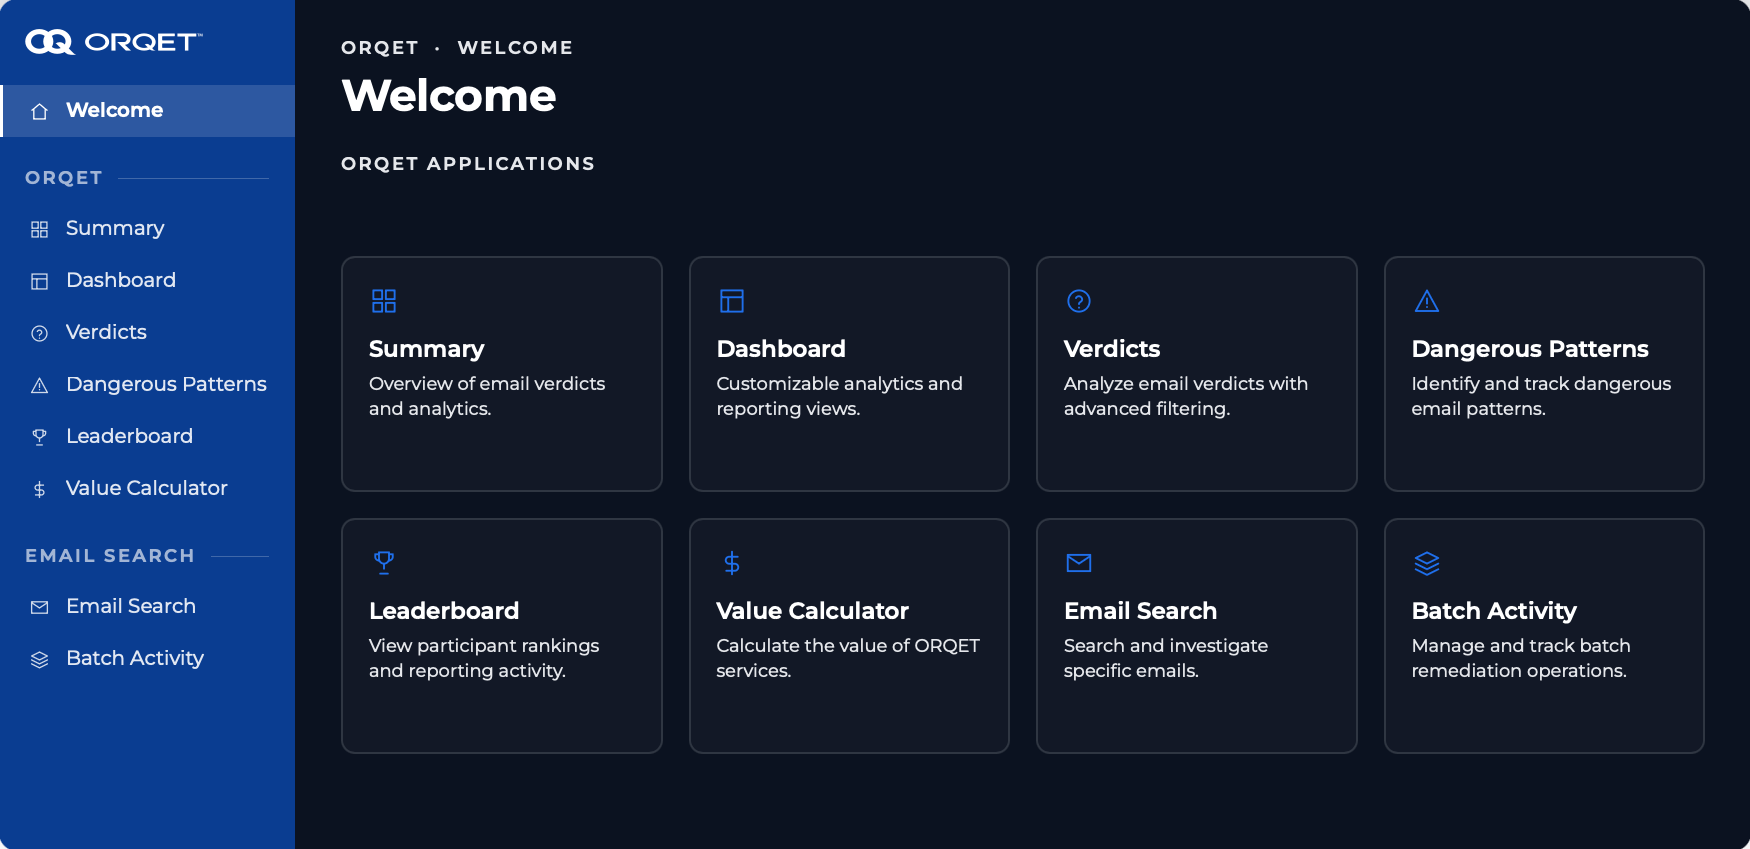
Representative interface shown with synthetic data. It does not reflect actual customer data or results. A live demonstration is recommended.
Analyze
Apply structured analysis to reported threats using platform capabilities and established workflows.
Validate
Produce consistent, explainable decisions supported by technology and human expertise.
Improve
Capture threat intelligence knowledge that strengthens future response efforts and organizational resilience.
Visibility That Builds Trust
Trust grows when security teams can see how their program is performing. ORQET provides visibility into how users are reporting suspicious emails, how actively they are participating, what is being confirmed malicious, and what action is being taken.
Interactive dashboards, historical reporting, attack pattern analysis, Search and Purge activity, and executive reporting provide a measurable view of post-delivery email activity across the organization. Teams can see what was reported, what was confirmed malicious, what was removed, user participation, and how those results change over time.
Whether reviewing a single reported email, a coordinated campaign, organization-wide user participation, or performance over time, ORQET gives security teams and leadership the visibility to understand what is happening across their Post-Delivery Email Threat Response program.
ORQET’s approach also aligns with principles outlined in the NIST AI Risk Management Framework.
The NIST AI Risk Management Framework recommends human oversight, documented accountability, and continuous monitoring across the AI lifecycle.
NIST AI Risk Management Framework 1.0, NIST AI 100-1, January 2023. Voluntary guidance.
These principles reinforce ORQET’s approach to AI-assisted technology, where human expertise remains behind every verdict.
The outcome: greater visibility into user participation, reported emails, confirmed threats, remediation activity, and program performance, giving security teams and leadership measurable insight into how their Post-Delivery Email Threat Response program is working.
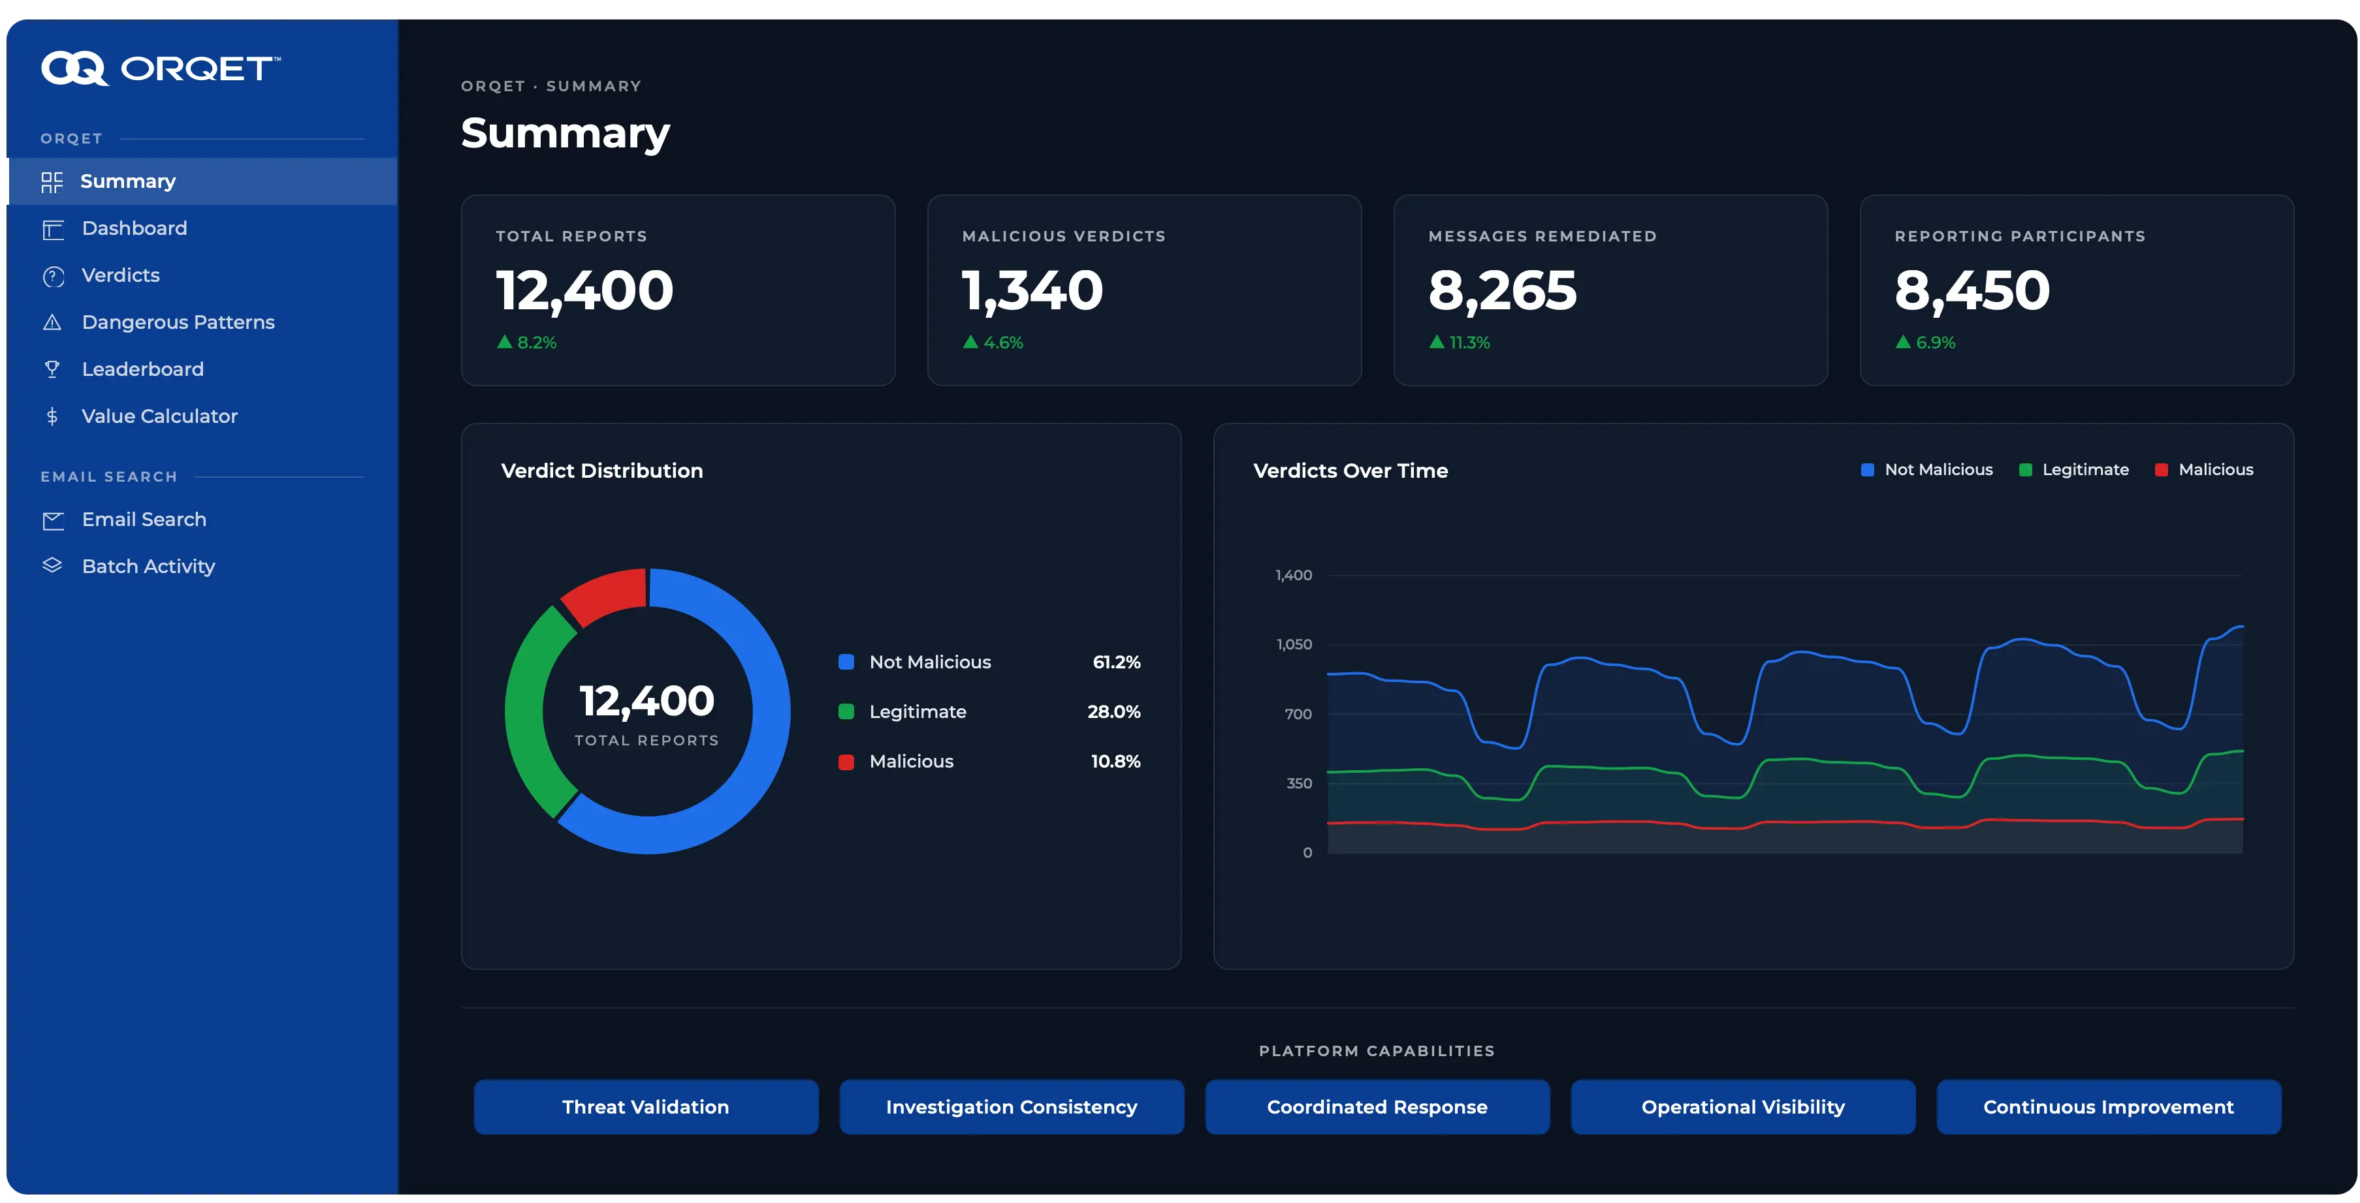
Representative interface shown with synthetic data. It does not reflect actual customer data or results. A live demonstration is recommended.
“The biggest change wasn’t speed. It was confidence. We stopped second guessing every verdict and started acting on them.”
Director, Security Operations, Manufacturing
Threat Intelligence Captured from Confirmed Attacks
Confirmed malicious emails move through four steps to turn attack data into actionable threat intelligence.
EXTRACT
IOCs are extracted from analyzed threats following a human-validated malicious verdict that results in a malicious verdict.
ENRICH
Contextual intelligence is added, including infrastructure data, hosting information, phishing artifacts, and related metadata.
PUBLISH
Enriched IOCs are published to the ORQET Threat Intelligence Platform.
PROTECT
Intelligence is delivered to customers and integrated systems, strengthening future detection, validation, and response.
EXTRACT
IOCs and other threat indicators are extracted from malicious emails through a human-derived verdict.
ENRICH
Indicators are enriched with additional context, including infrastructure data, hosting information, phishing artifacts, and related metadata.
PUBLISH
Enriched indicators and investigative context are published to the ORQET Threat Intelligence Platform, creating tactical and technical threat intelligence available to ORQET customers.
SHARE
Threat intelligence can be shared through ORQET’s API and STIX/TAXII feed with security systems capable of consuming it, extending intelligence from confirmed attacks beyond the original investigation.
Core receives IOC reporting by email. Advanced and Inline include Threat Intelligence Platform access. Platform API access for external systems is an optional add-on.
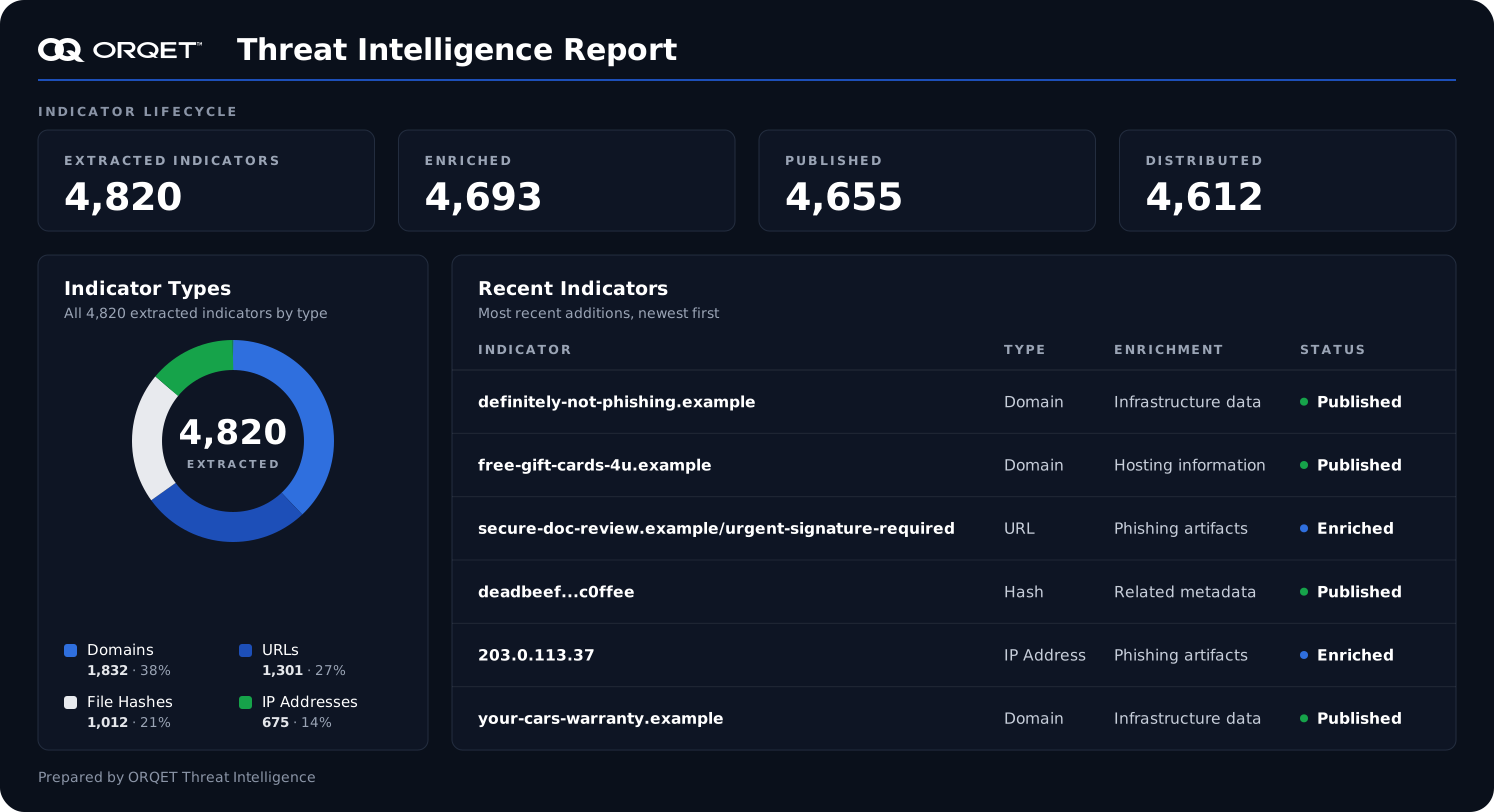
Disclaimer: This dashboard is intended for marketing and informational purposes only. The data shown on the report is synthetic data and it does not reflect actual customer data or results.
Built to Strengthen Your Security Ecosystem
No two security programs look alike. Each environment reflects investments in people, processes, and technology, and ORQET is designed to work alongside the security technologies organizations already rely on.
ORQET operates within Microsoft 365 and Google Workspace and works alongside Microsoft Defender for Office 365, secure email gateways, SIEM, SOAR, EDR/XDR, threat intelligence platforms, and security awareness programs. ORQET provides Post-Delivery Email Threat Response after a suspicious email is reported, without requiring organizations to replace their existing security technologies.
Confirmed threats also generate tactical and technical threat intelligence that can be shared through ORQET’s API and STIX/TAXII feed with security systems capable of consuming it.
Our Ecosystem:
As security programs evolve, ORQET provides a dedicated Post-Delivery Email Threat Response capability that can operate alongside the technologies already in place.
Measurable Impact Across, Your Response Program
ORQET brings the post-delivery response process together in a way security teams can see, measure, and demonstrate. From the initial verdict through remediation and threat intelligence, each part of the process contributes to a more effective response program.
The result: measurable outcomes security leaders can use to demonstrate the impact and value of their Post-Delivery Email Threat Response program.
Ready to Strengthen Your Post-Delivery Email Threat Response?
See how ORQET works alongside your security environment to deliver human-derived verdicts, automated remediation, greater visibility, and tactical and technical threat intelligence.
Whether you are evaluating your current approach or looking to improve what happens after a suspicious email is reported, our team can show you how ORQET fits within your environment and supports your Post-Delivery Email Threat Response program.